What broke
Missing IDs weakened retry checks.
Some events arrived without provider IDs, while one short token lifetime was stretched across immediate WebSocket admission and delayed callbacks.
DentSignal repair · Webhook trust
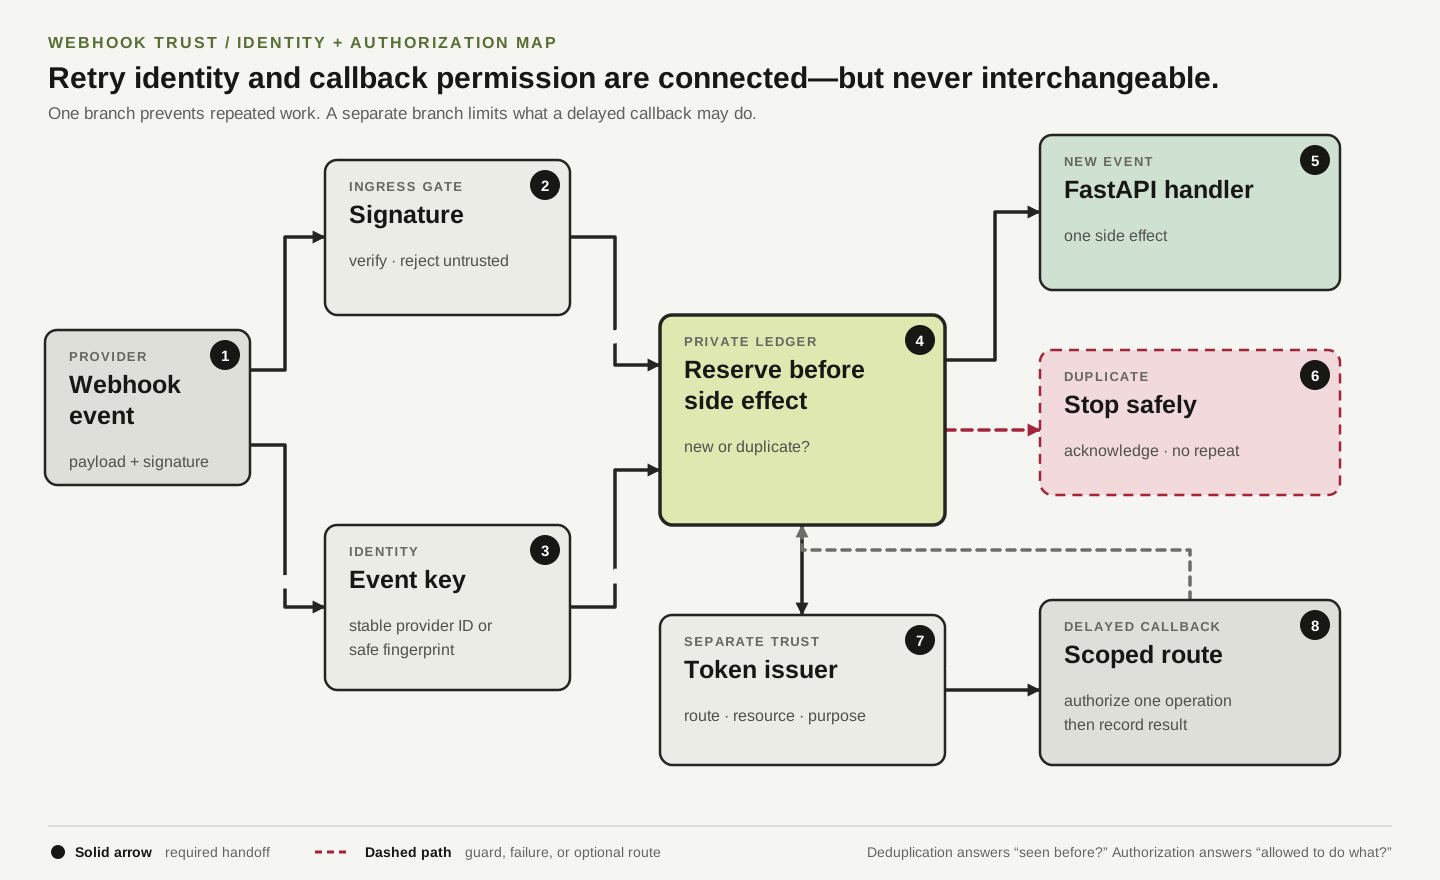
The repair gave every incoming event a stable identity and separated delayed callback trust from immediate socket admission.
What broke
Some events arrived without provider IDs, while one short token lifetime was stretched across immediate WebSocket admission and delayed callbacks.
What changed
Missing IDs receive a stable fallback fingerprint. Callback tokens bind to one route, one resource, and a purpose-specific lifetime.
What it fixed
Stable event identity supports deduplication while delayed callbacks no longer reuse the short-lived socket-admission token.
Before / after
process(payload)
reuse(socket_token)event_key = provider_event_id or fingerprint(payload)
dedupe(event_key)
callback_token = issue_token(
scope="callback", resource=call_id)Evidence
The historical repair record shows stable fallback identity for missing provider IDs and purpose-scoped callback tokens with distinct lifetimes. Static checks and secret/external-service guards supported the change, but the page does not turn old test counts into a current security claim.
Stack and capabilities
Next